From thousands of alerts to the few that matter.
Alertio unifies detection, investigation and response in one security operations platform. It ranks every alert by real risk, reconstructs attacks across your environment, and puts containment one click away — so your analysts spend their time stopping threats, not sorting noise.
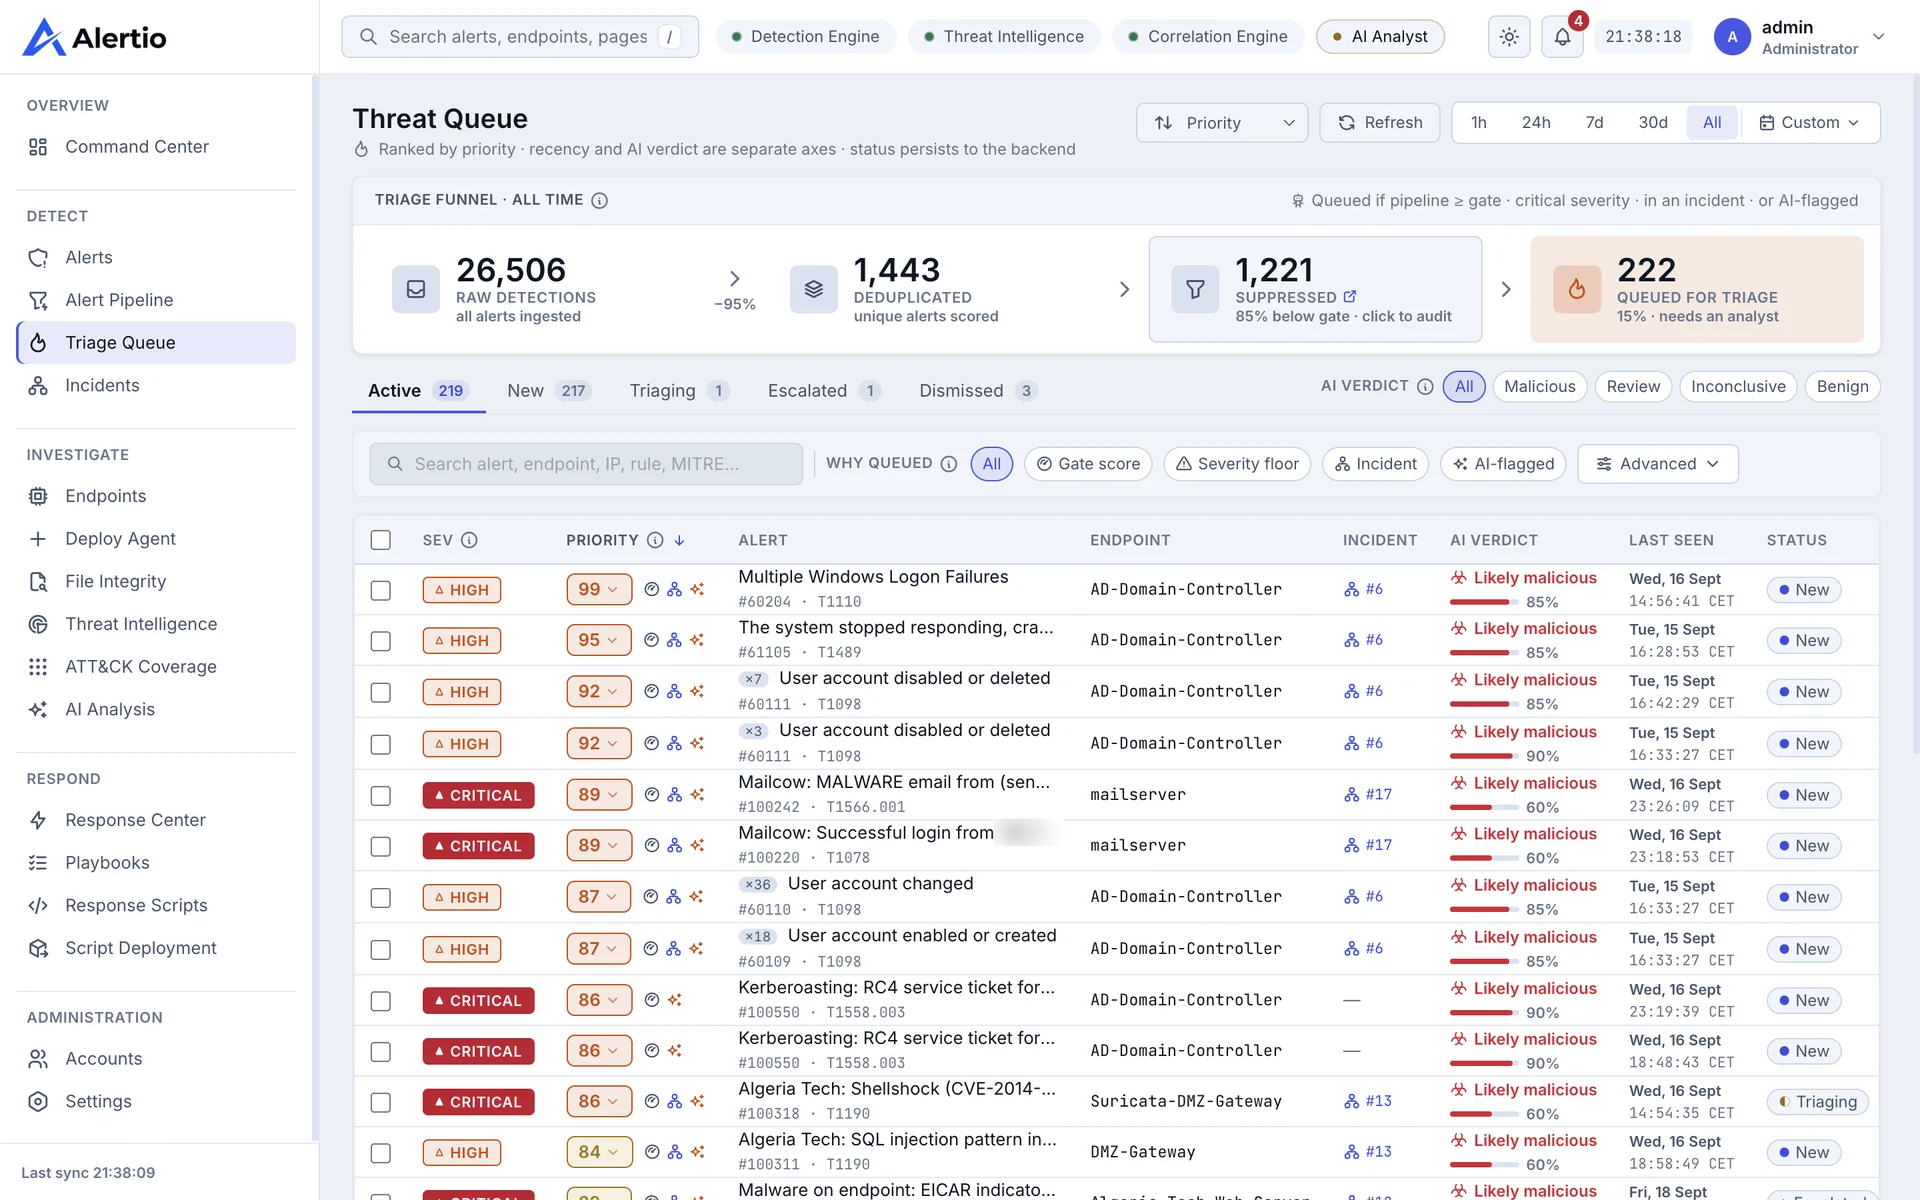
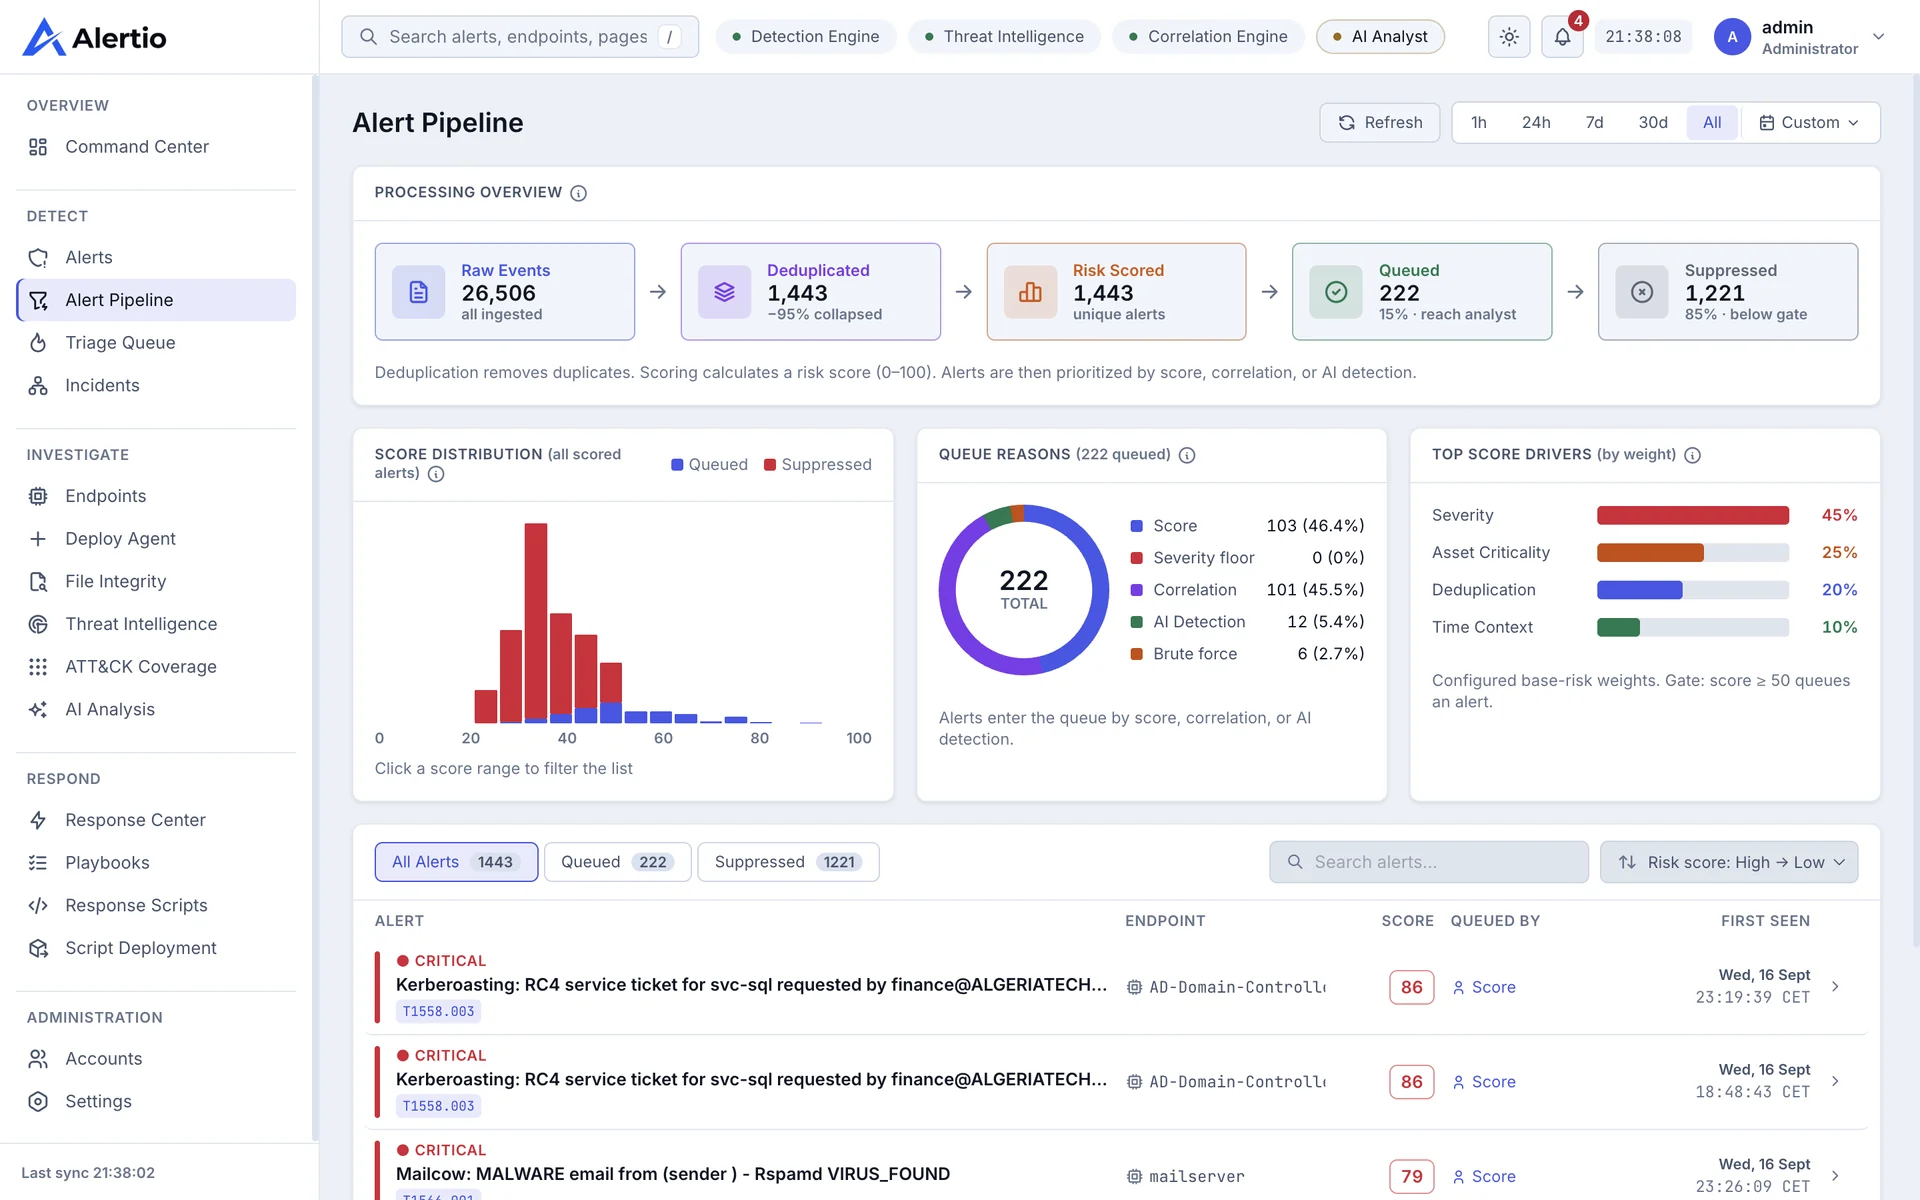
Measured during a live, multi-stage attack simulation: 26,506 raw security events reduced to 222 prioritised alerts. Every suppressed event is retained and auditable.
One attack, from first alert to contained threat.
Watch Alertio score a single alert, connect it to the attack it belongs to, explain what happened in plain words, and contain it, using real data from our validation lab.
Security teams don't lack alerts. They lack time.
A modern environment produces thousands of security events every day. Most are routine, many are duplicates, and the handful that signal a real attack look exactly like everything else. A severity rating alone cannot tell a test laptop from a domain controller, or a single failed sign-in from a coordinated campaign.
Alertio adds the context every alert is missing, and turns a flood of events into a short list of decisions.
- Alert fatigue
- Analysts lose hours clearing duplicates and routine noise, while the alert that matters waits in the same queue as thousands that don't.
- Severity without context
- A static severity score ignores what was hit, how often it has happened, and what happened just before it.
- Attacks hide in fragments
- Reconnaissance, stolen credentials and privilege escalation arrive as unrelated alerts on different machines. Nobody sees the full picture until it is too late.
- Response is slow and manual
- Containing a confirmed threat means switching tools, running scripts by hand and keeping a change log on the side.
One platform, from first signal to contained threat.
Alertio takes every alert through the same four stages, and shows the analyst the reasoning at each one.
-
01
Prioritise
Duplicates are collapsed and every alert is scored from 0 to 100 on severity, asset criticality, repetition and timing. Only what deserves attention reaches the queue.
-
02
Correlate
Related events are linked into incidents and mapped to the kill chain, so a quiet alert that belongs to an attack is never missed.
-
03
Investigate
Every incident arrives with its evidence, blast radius, threat intelligence and an AI-written attack narrative.
-
04
Respond
Block, isolate, terminate or quarantine directly from the incident. Every action is previewed, approved, logged and reversible.
Prioritisation your analysts can trust.
Every alert receives a risk score from 0 to 100, built from four weighted factors. The calculation is shown for every alert and the weights are configurable from the console: transparent by design, with no black box and nothing to retrain.
- Context-aware scoring. Rule severity 45%, asset criticality 25%, repetition 20% and time context 10% by default, each adjustable to your environment.
- Noise removed first. Identical events are grouped before scoring, so a single noisy rule can never flood the queue.
- Critical alerts never wait. A severity floor guarantees the most serious detections reach an analyst, whatever their score.
- Nothing is lost. Suppressed alerts remain searchable and auditable, and are brought back automatically when they become part of an incident.
See the whole attack, not scattered alerts.
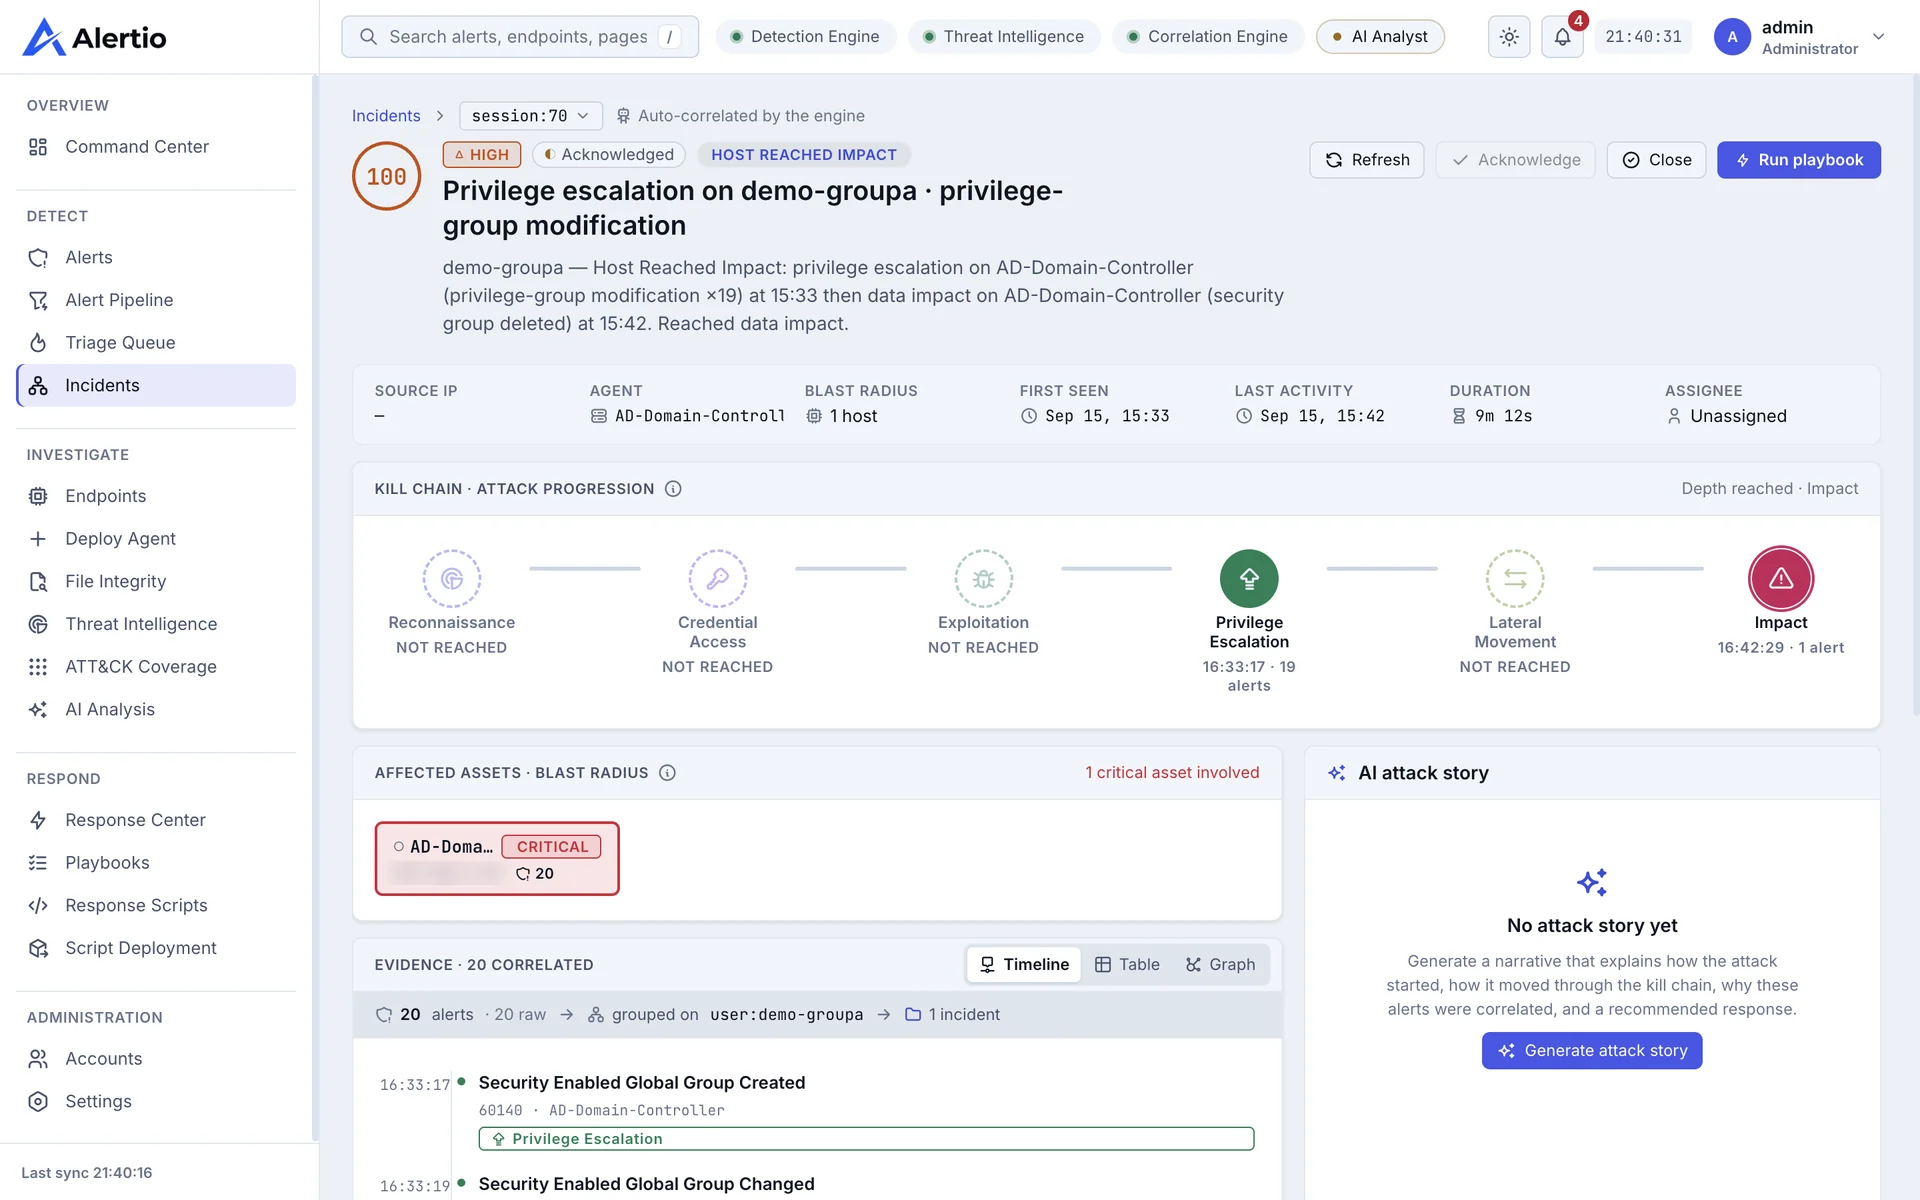
The correlation engine links related events across machines, sensors and network zones into a single incident, and maps it onto six kill-chain stages, from reconnaissance to impact. Your team sees how far an intrusion has progressed, not just that something happened.
- Seven built-in attack patterns. Multi-stage attacks, scan-and-exploit, credential attacks, lateral movement and more, defined as configuration so new patterns need no code.
- Identity-aware correlation. Incidents follow the compromised account across machines and network zones, where IP-based correlation would split one attack into several.
- Blast radius at a glance. Affected assets and their criticality, with every correlated alert available as a timeline, a table or a graph.
- AI attack narrative. A security-specialised language model explains how the attack unfolded and recommends next steps, ready for analyst review.
Know exactly where you're exposed.
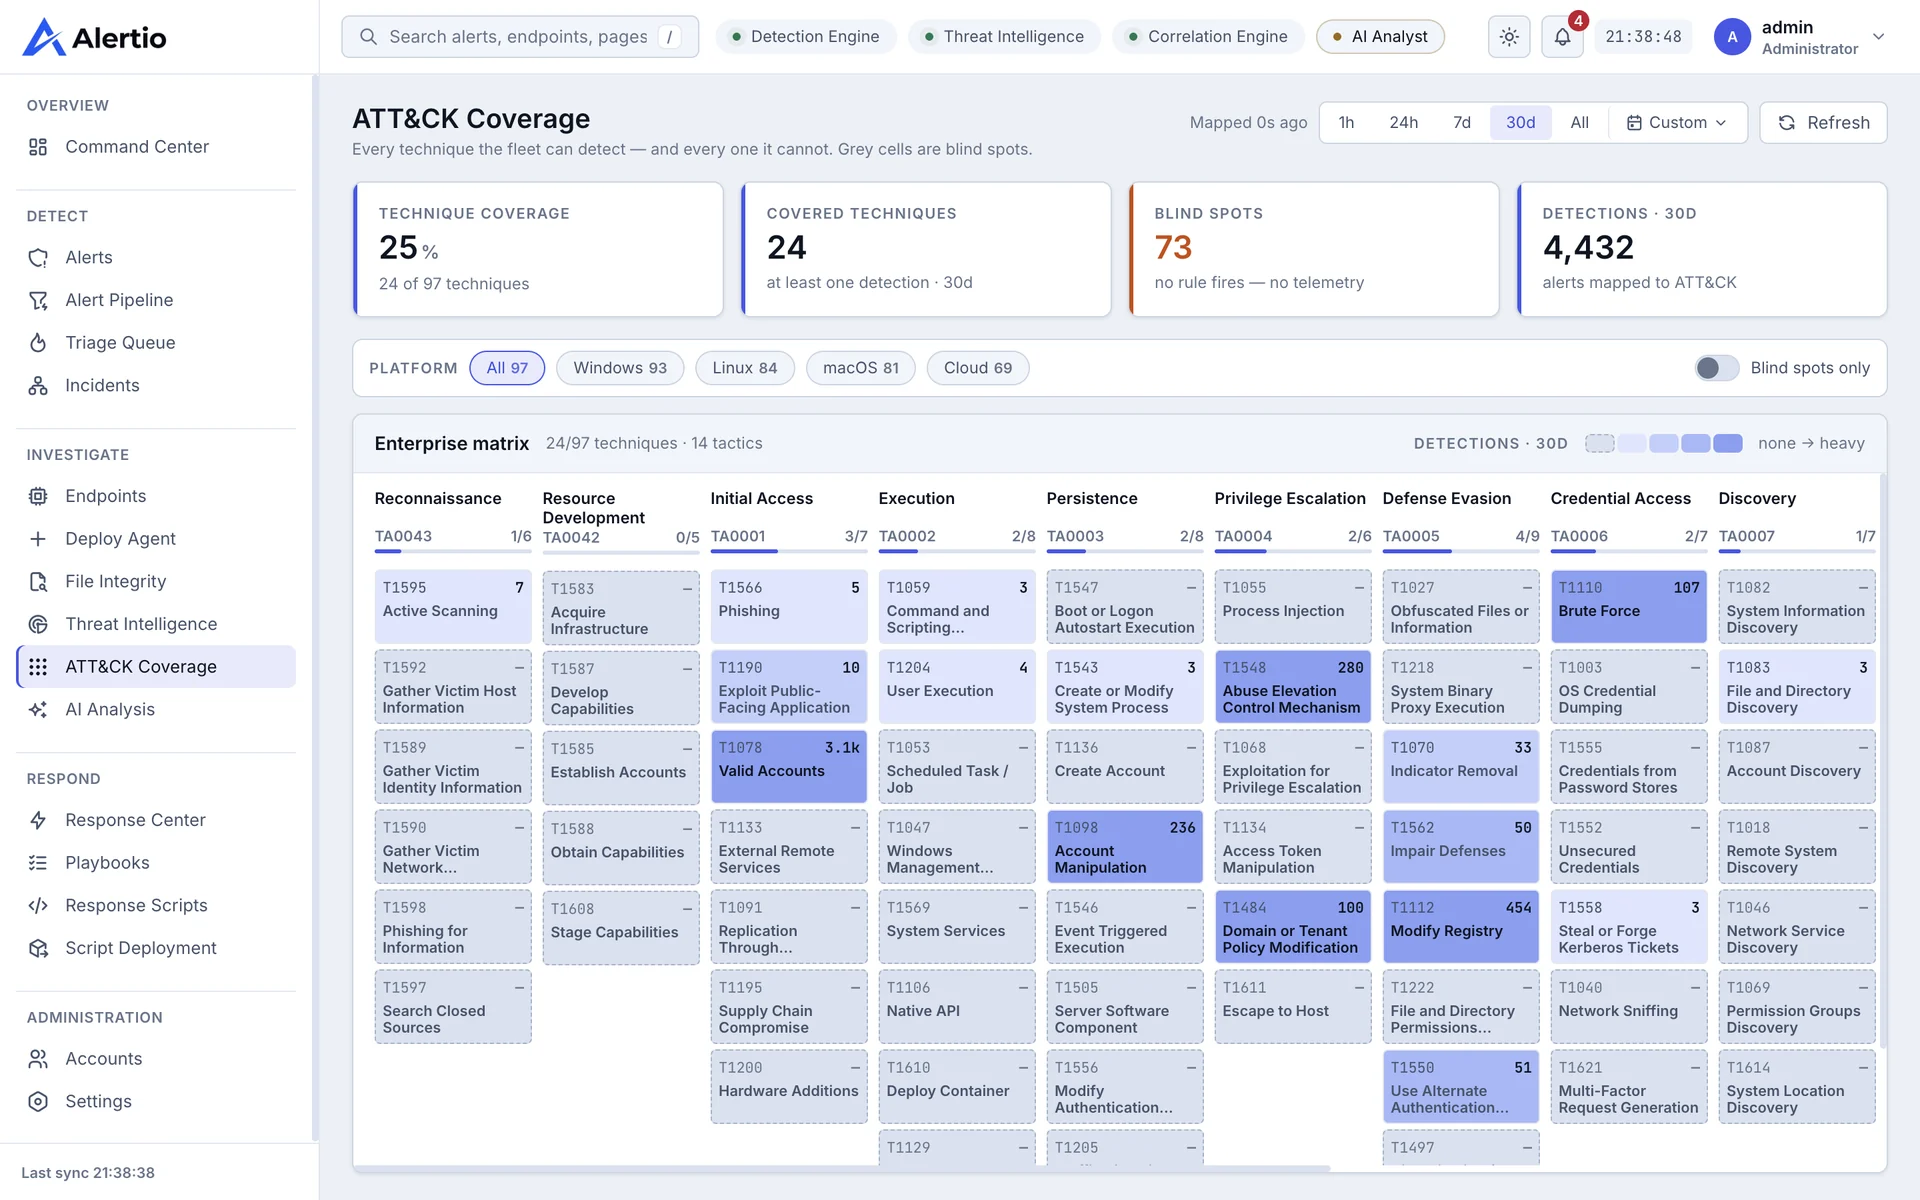
Every detection is mapped to MITRE ATT&CK. A live coverage matrix of 14 tactics and 97 techniques shows what your environment actually detected in any period, and highlights the techniques where you are blind.
- Measured, not assumed. Coverage is calculated from the alerts your sensors actually raised, for any time window you choose.
- Blind spots on demand. One switch isolates every technique no detection has fired on: a ready-made detection engineering backlog.
- Filter by platform. Windows, Linux, macOS or cloud, so engineering effort goes where the gaps are.
- Weighted by activity. Each technique is shaded by detection volume, from a single hit to thousands.
Everything an analyst needs, in one place.
Alertio brings the context to the alert, instead of sending analysts across five tools to find it. Threat intelligence, endpoint details and AI analysis sit right beside the evidence.
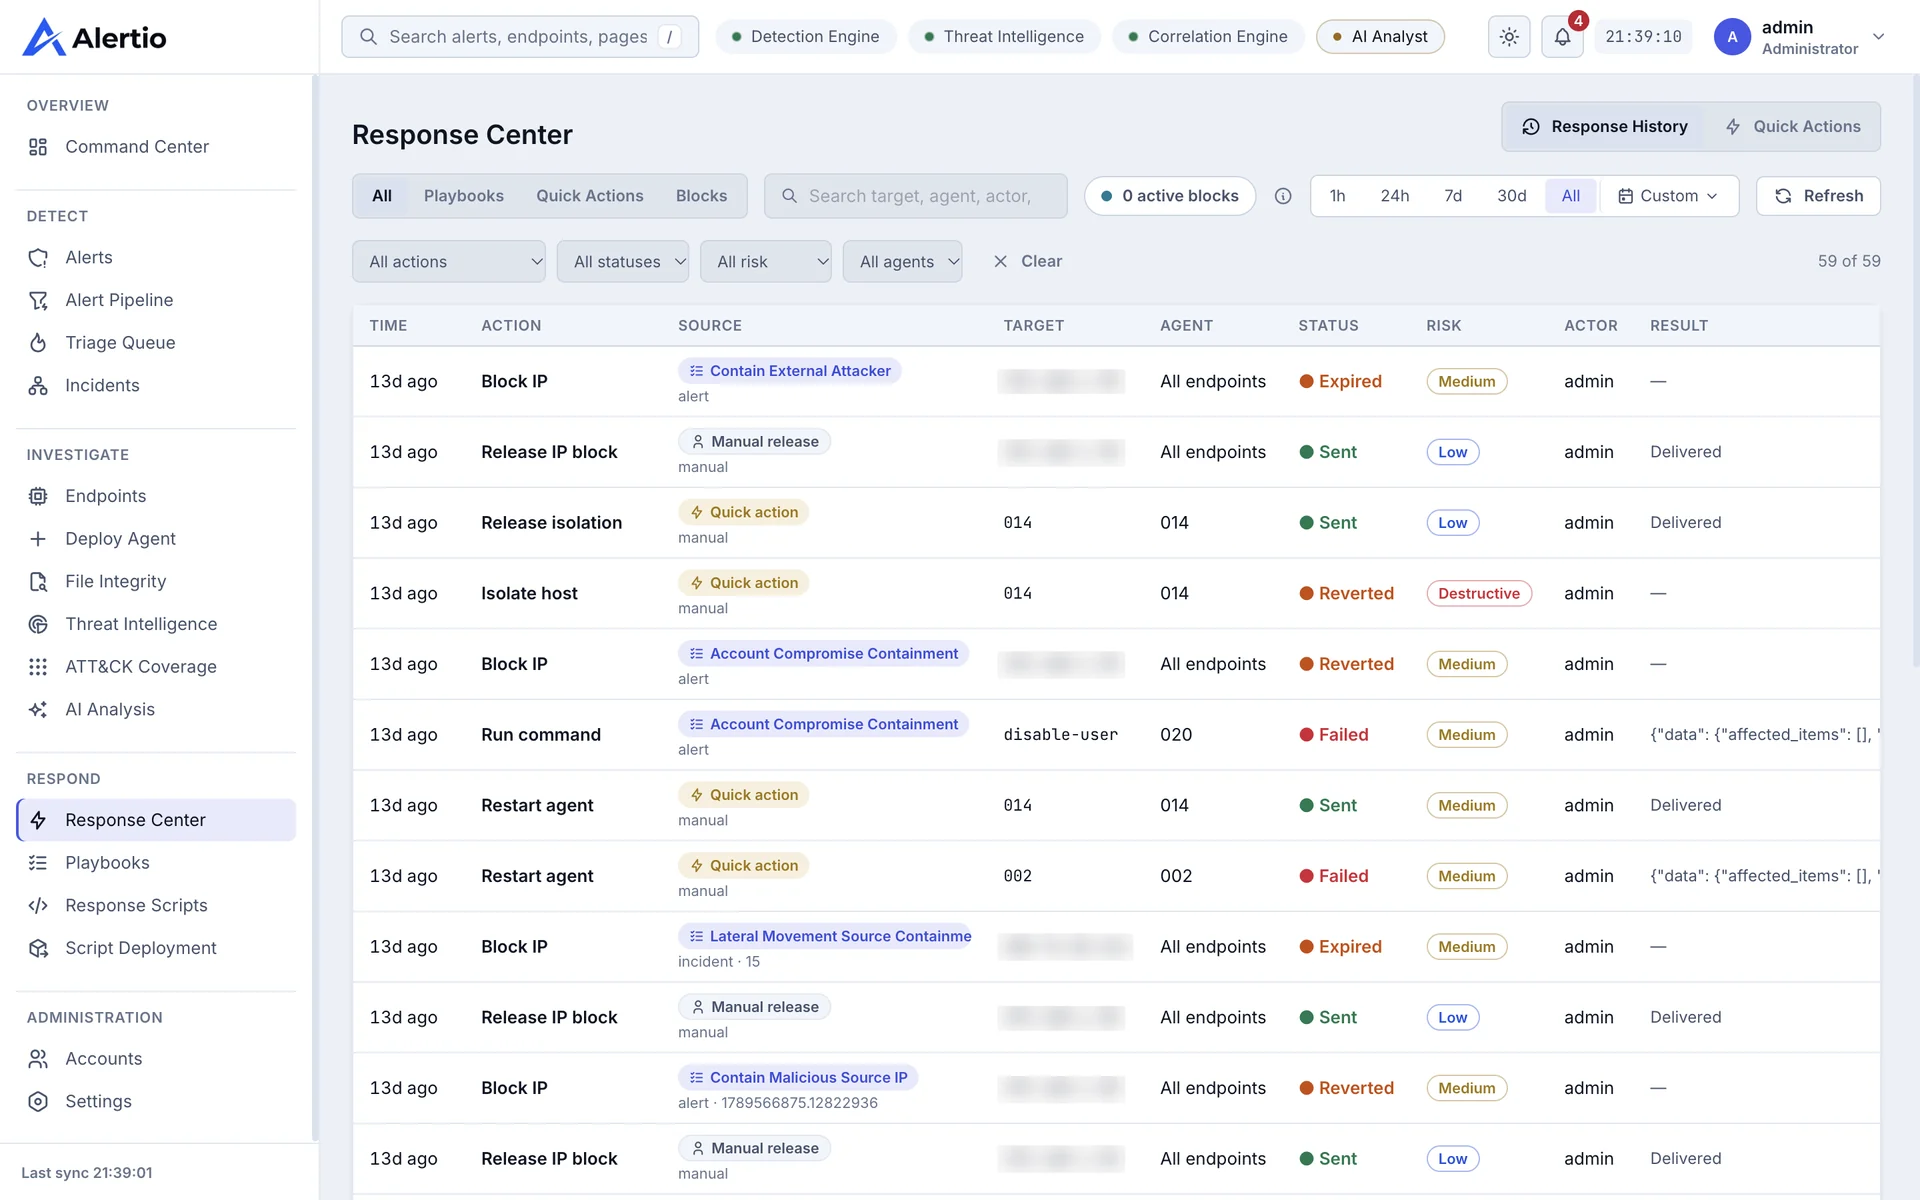
- Integrated threat intelligence. Check any file hash, IP address, domain or URL against VirusTotal, with every lookup kept in a searchable history.
- AI-assisted triage. Foundation-Sec-8B, a security-specialised model, returns a verdict, a confidence level and the evidence behind it. Analysts confirm or override, and agreement is tracked over time.
- Private by design. The model can run entirely on your own infrastructure, and an analysis runs only when an analyst requests it.
- Full endpoint context. Each host's alerts, vulnerabilities, configuration assessment, file integrity changes and response history, in a single view.
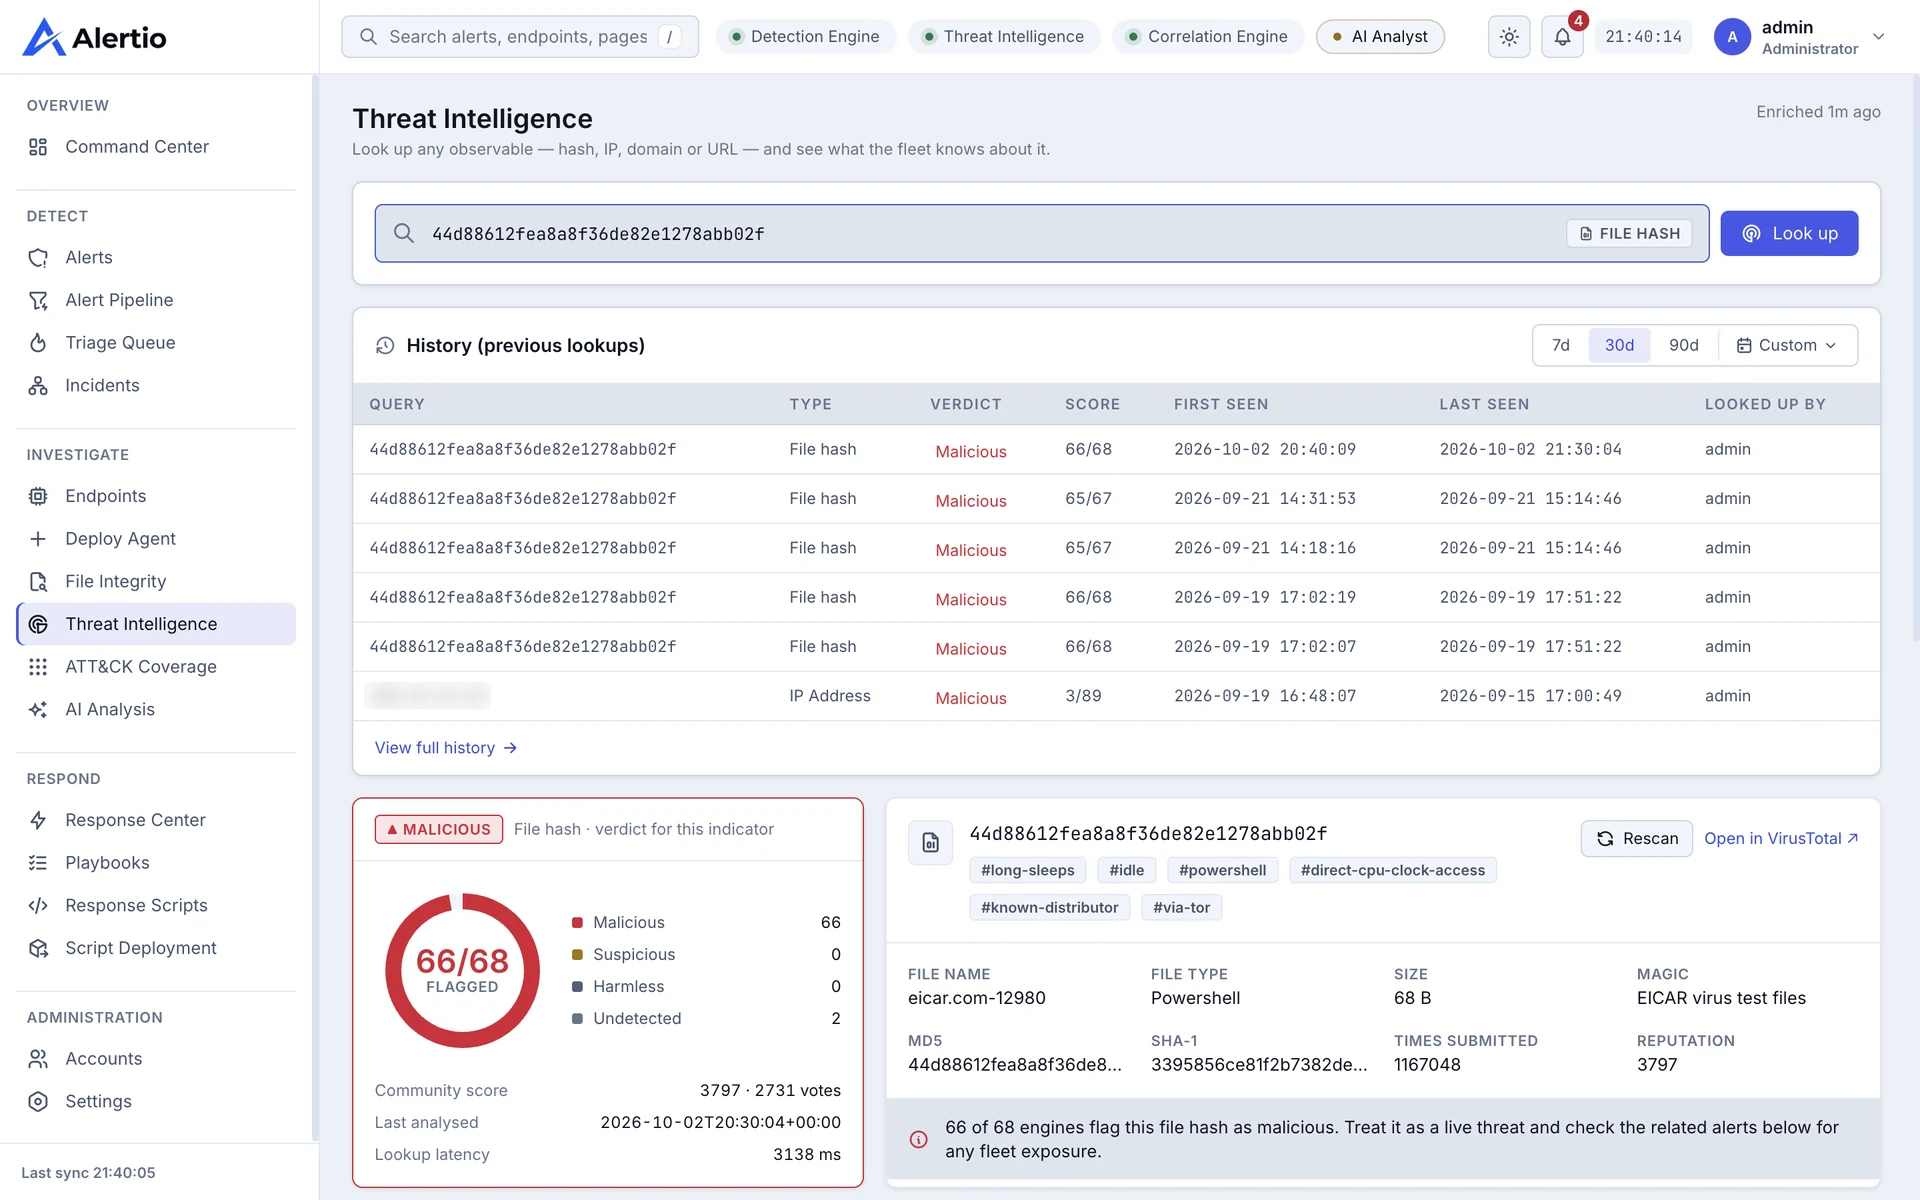
Contain threats from the screen where you found them.
When an incident is confirmed, Alertio carries the decision straight to the endpoint through lightweight agents — from a single quick action to a multi-step playbook, launched from the incident itself.
- Eight response actions. Block or unblock an IP, isolate or release a host, terminate a process, quarantine a file, restart an agent or run a command.
- Playbooks. Turn your procedures into repeatable, multi-step playbooks your team runs in one click.
- Safe by design. Every action is previewed and requires explicit confirmation. Destructive actions are reserved for administrators.
- Reversible and fully audited. Blocks expire automatically, actions can be rolled back, and every run records who did what, when, and with what result.
Deploy, extend and monitor from the same console.
The operational tooling a security team needs around detection, built in rather than bolted on.
Custom response scripts
Author scripts in a built-in code editor, scan them for errors and dangerous commands, test them in a sandbox, then sign and deploy them to your endpoints, with verified deployment status for every agent.
Agent deployment
Guided installation for Windows, Linux and macOS, single-use enrolment tokens, and ready-made Ansible bundles that roll agents out across an Active Directory domain.
File integrity monitoring
Know what changed, where and when on every monitored path, with policies managed centrally and each change mapped to its stage of the attack.
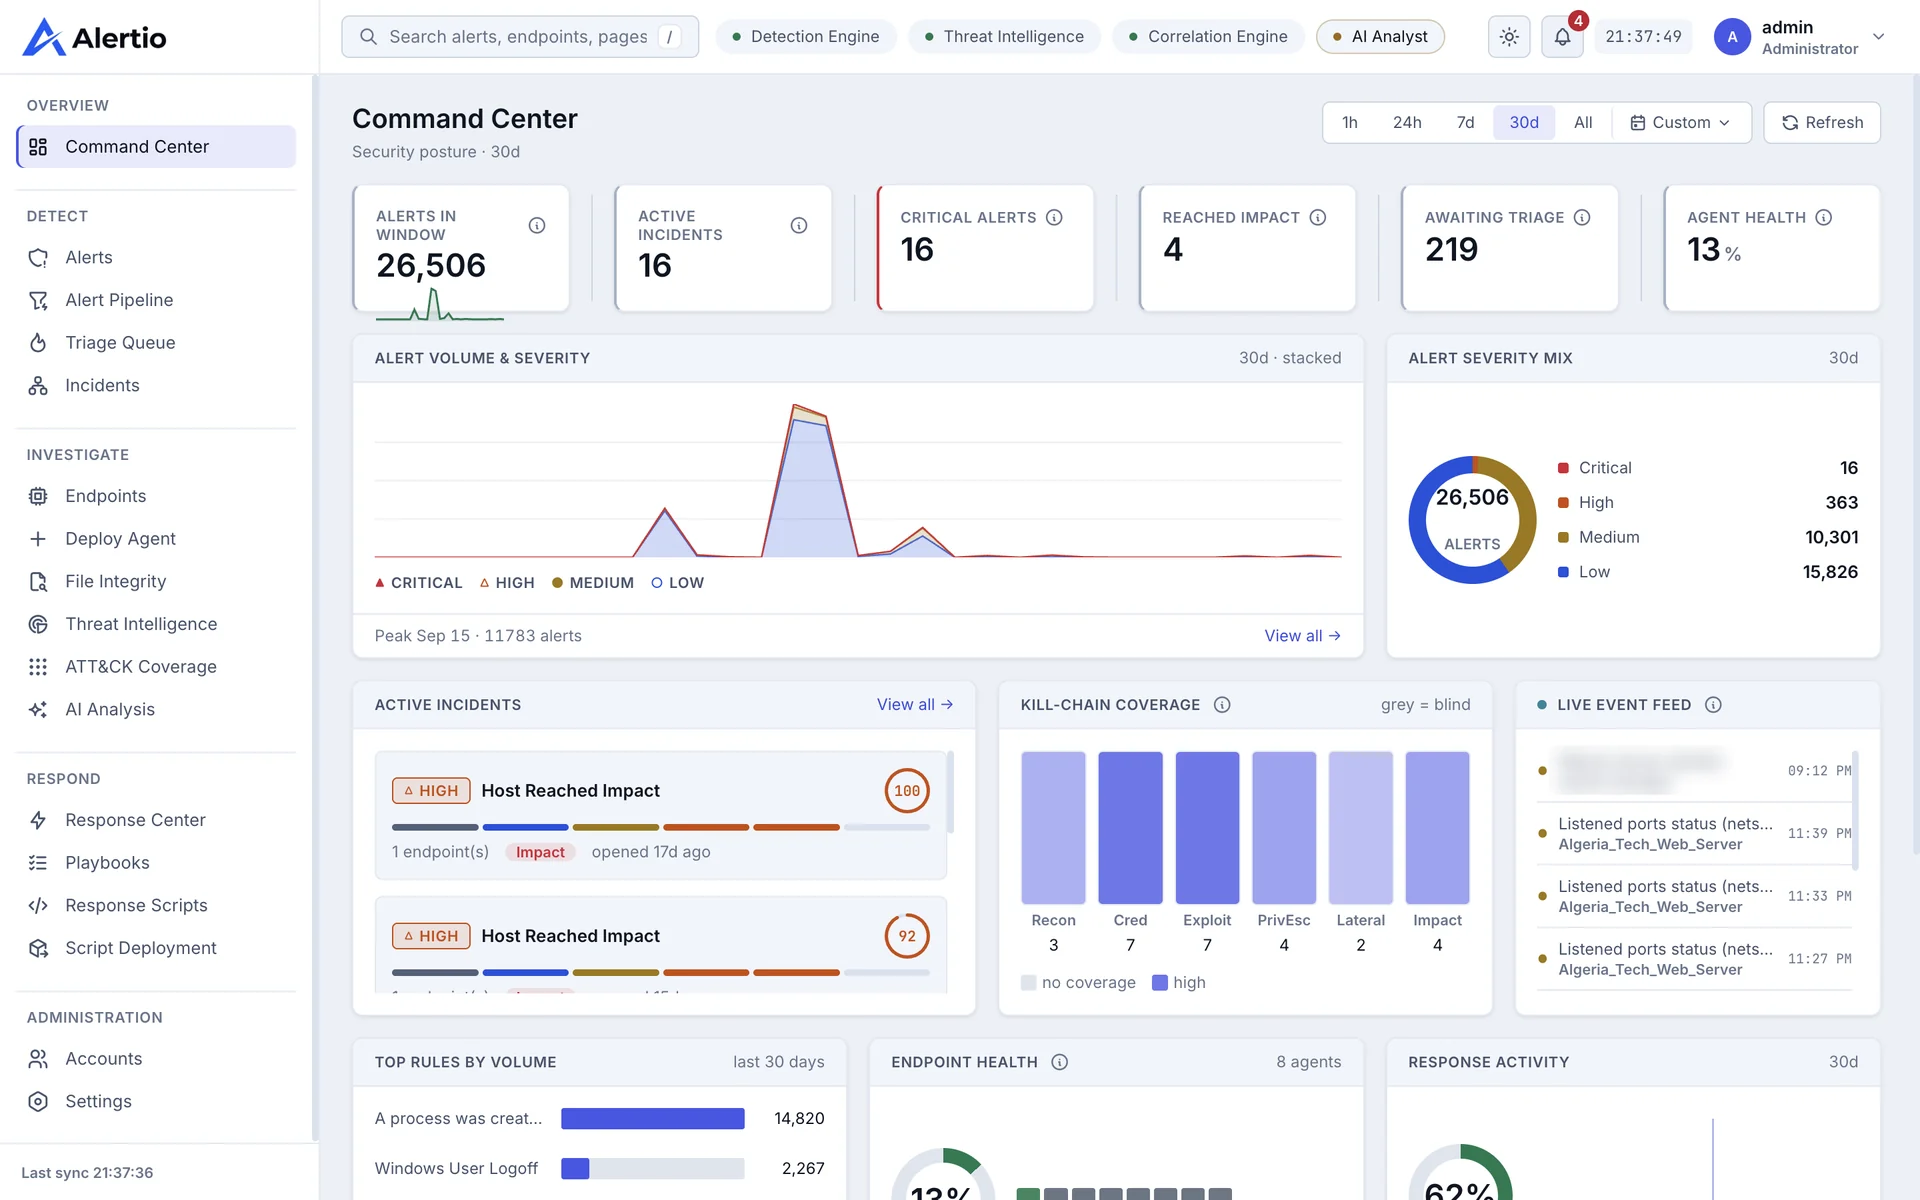
Your entire security posture, live, on one screen.
Alert volume and severity, active incidents, kill-chain coverage, endpoint health and response activity, all driven by a single time filter, from the last hour to all time.
- Role-based access
- Administrator, Analyst and Read-only roles, enforced in the interface and independently at the API.
- Built-in notifications
- Critical alerts and response activity surface in a notification centre, without leaving the console.
- Designed for daily use
- One time filter, one severity language and global search across every screen, in light and dark themes.
Your infrastructure. Your data. Your decisions.
Alertio deploys on-premise, inside your network, so sensitive security data never leaves your control, and people stay in charge of every action that matters.
- Deployment On-premise · containerised
- Tenancy Dedicated single-tenant
- Endpoints Windows · Linux · macOS
- Data sources Endpoint · network · mail · directory
- Threat intelligence VirusTotal
- AI model Foundation-Sec-8B · self-hostable
- Framework MITRE ATT&CK
- Access control Role-based · three roles
- Human in the loop
- Playbooks run only when an analyst launches them. For a platform that can isolate a host, that is a deliberate safety guarantee.
- AI that advises, never decides
- Every AI verdict is recorded as a recommendation an analyst can override. It never closes an alert or triggers a response on its own.
- Open and extensible
- MITRE ATT&CK as the common language of attacks, and a connector layer that lets new data sources plug in as your environment grows.
See Alertio on your own data.
Book a walkthrough with our team. We will show you how Alertio would prioritise, correlate and respond to the alerts your team handles today.